Security and backups
Sessions
Access tokens are valid for 15 minutes; refresh tokens are random, stored only as hashes and replaced on every use. Reusing an old one ends the session. Signing out, a password change or deactivating a user takes effect at once.
Two-factor sign-in
The second factor is a one-time code per RFC 6238 (TOTP) from an authenticator app. It is requested after the password or after the code sent by e-mail. During setup the person receives recovery codes for the case that the device is missing.
The firm sets in the settings who needs a second factor: nobody, portal users only or everyone. Anyone who has not set it up yet gets a session that allows only the setup. An administrator can reset a person's second factor.
Audit log
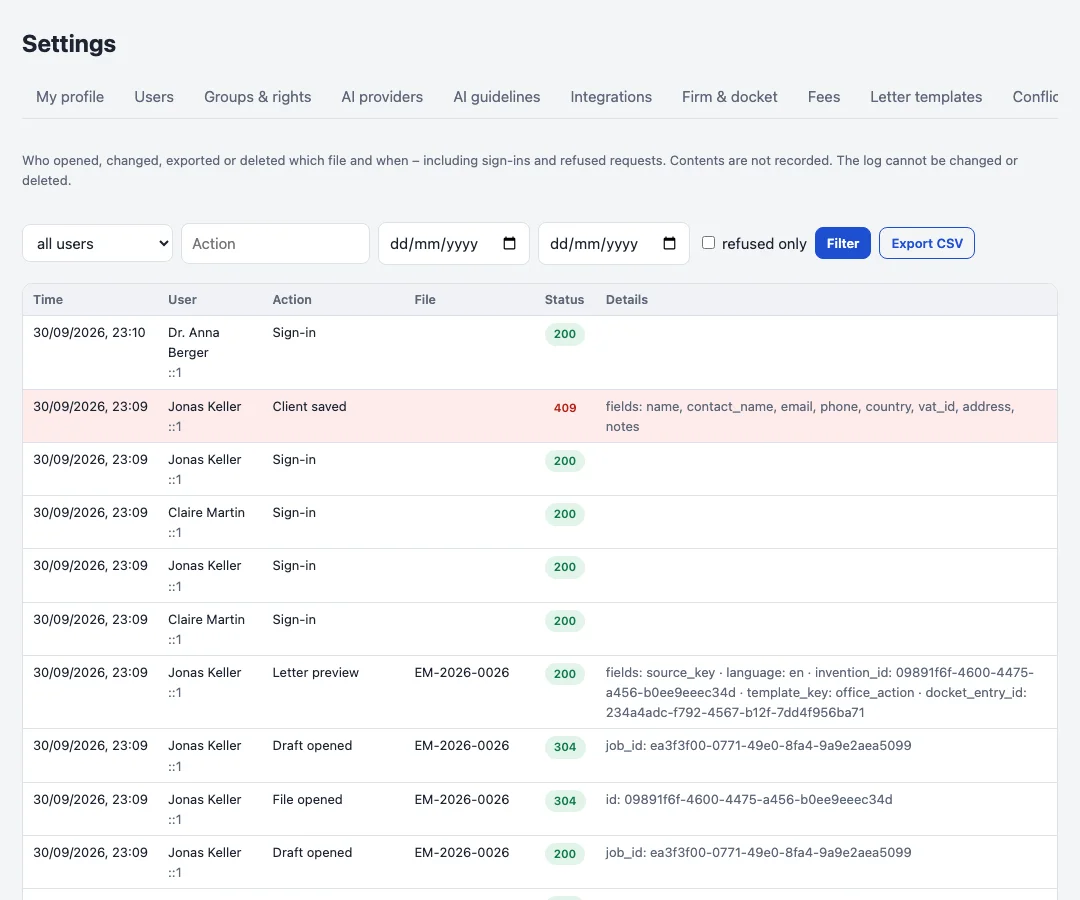
Every write, every opened file and every export or download is recorded with user, file, result and address, including refused requests and sign-ins. Only identifiers are stored, no contents; the database refuses to change or delete entries.
Backups
The backup container writes an encrypted file with the database dump and all files every night and keeps them for a configurable number of days. Every week (by default) it restores the newest one into a scratch database and compares the row counts. Restoring on the server is a single command that first backs up the current state.